Open-sourcing awsjail - a login shell that only accepts aws ... commands. Users use standard SSH, land at an awsjail:<account-id>:<user> > prompt instead of bash, and can run scoped AWS CLI commands and nothing else. No shell or OS command access, no keys handed out, no internet access from the terminal with every command logged.
Slides and demo video from my talk at CyBe AI Summit 2026 (4th Sept, Bangalore) on Excessive Agency in context of AI Agent Execution - reconstructed from a real pentest where a “helpful” AI agent was the door in, chaining a debug tool, container access, a neighbouring internal agent, and overprivileged AWS IMDS creds into full cloud account compromise.
Slides and some background of my talk at Vulncon Bangalore (June 2026) on how I convinced Amazon Q to perform an authorization check on itself, its tools and the results of that exploration. Interesting findings overall around IAM boundaries and tool/capability privileges.
A blog post about some post exploitation scenarios with MySQL, MSSQL, PostgreSQL and Oracle that use SQL Injection to make network requests resulting in Server Side Request Forgery/Cross Site Port Attacks.
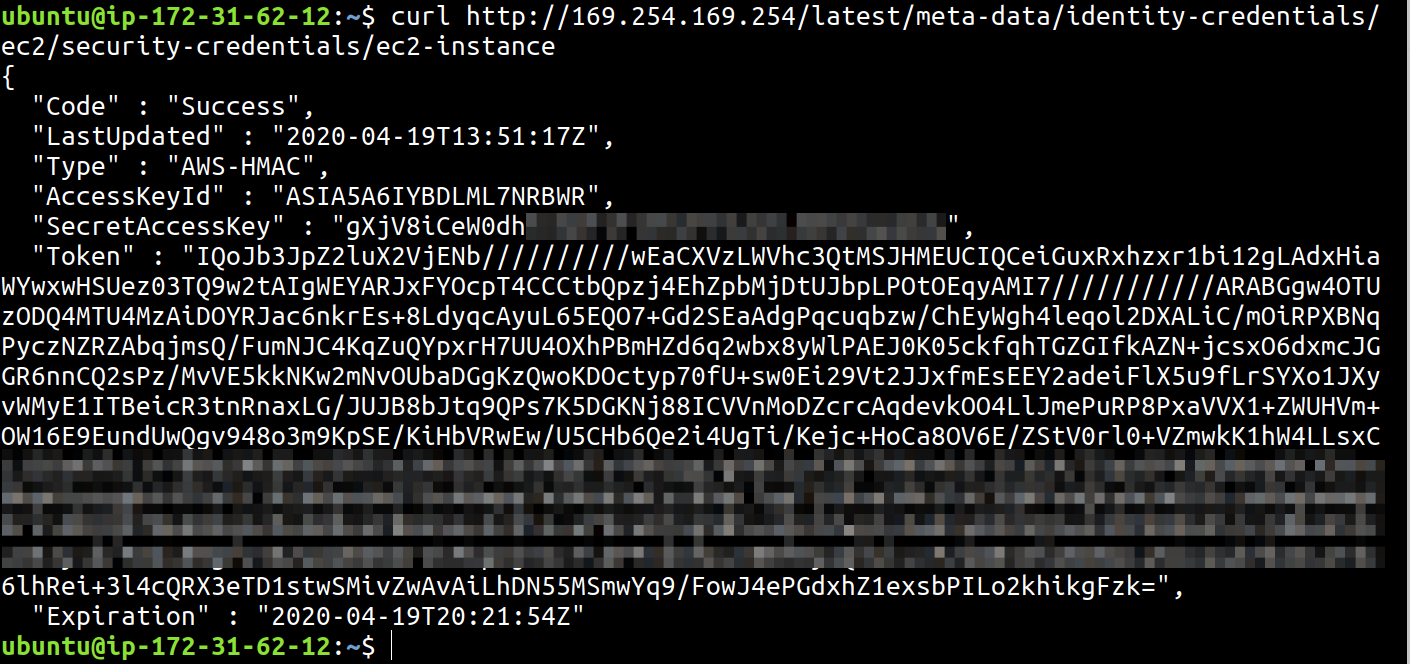
A quick blog post to investigate what instance-identity security credentials are that can be generated using the metadata instance on every EC2 instance in AWS, even when no role is attached to the instance.
Slides of my talk on using mis-configurations, overtly permissive IAM policies and application security vulnerabilities to get shells in AWS EC2 instances and go beyond the plane of attack. Presented at OWASP Bay Area August 2019 meetup.